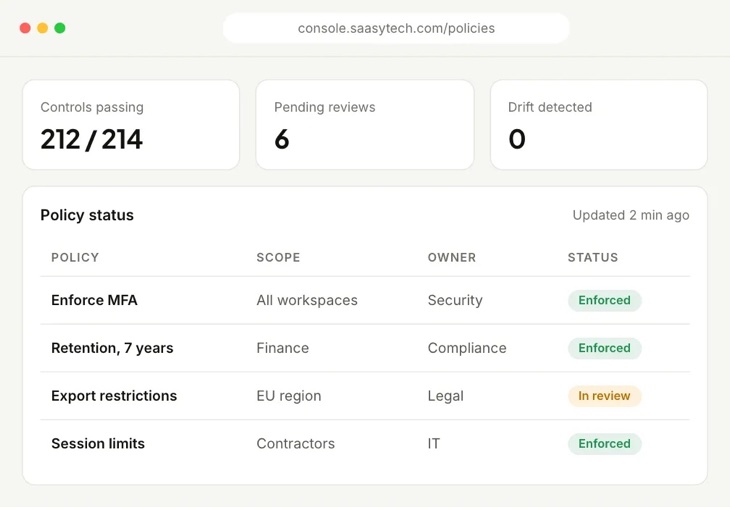
Enforced
Encryption everywhere
AES-256 at rest and TLS 1.3 in transit, with optional customer-managed keys.
Loading
Govern access, automate approvals and prove compliance from one platform, with the security posture your auditors, CISO and board expect.
Independently audited and certified
Access matrix
| Role | Read | Write | Export | Admin |
|---|---|---|---|---|
| Admin | ||||
| Editor | ||||
| Auditor | ||||
| Viewer |



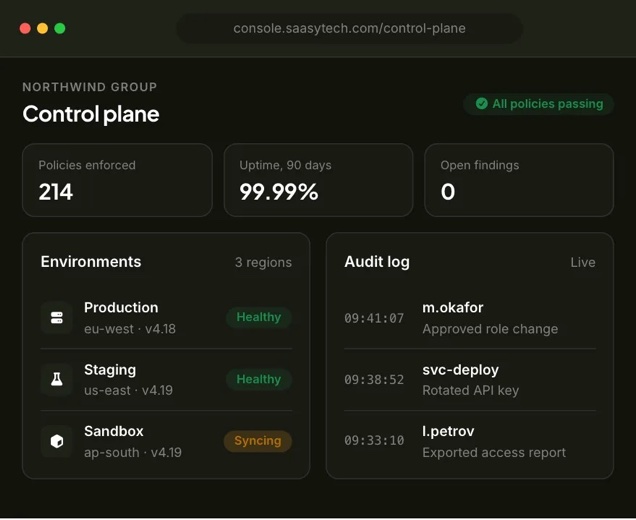
Every capability shares the same identity layer, policy engine and audit trail, so control scales as fast as your organisation does.
Define guardrails once and apply them to every workspace, region and business unit. Changes are versioned, reviewed and reversible.
Connect your identity provider, provision users automatically and give people only the access their role requires.
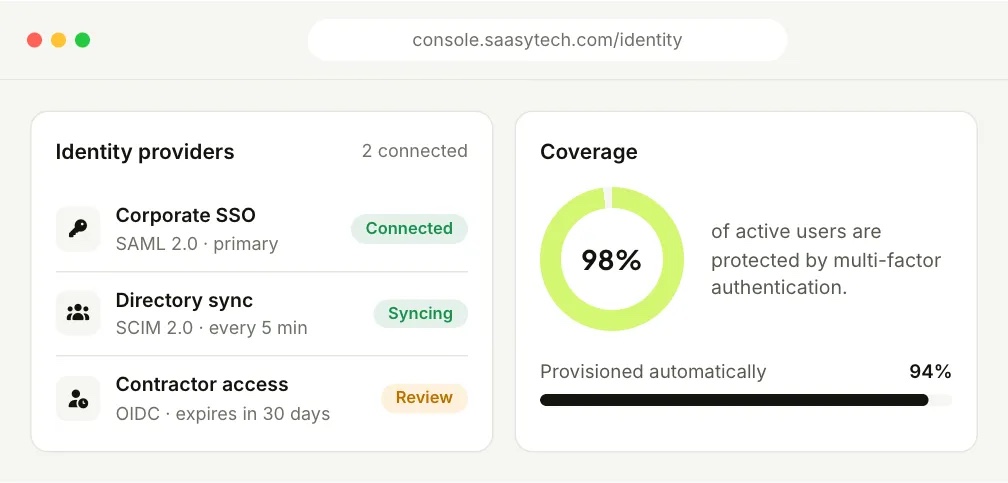
Replace email chains with routed workflows. Each step records who decided what, when and why, ready for the next audit.
Track service levels, usage and unusual behaviour across the whole organisation, then stream the signals into your own tooling.

Controls are monitored continuously and tested independently. Request our reports under NDA at any time.
AES-256 at rest and TLS 1.3 in transit, with optional customer-managed keys.
Mandatory strong authentication with phishing-resistant options.
Keep data in the region you choose, across 14 hosting locations.
Tamper-evident records retained for up to ten years and exportable.
Continuous scanning with defined remediation times for every severity.
Independent testers probe the platform and share results with customers.
Certifications and attestations
Six capabilities that procurement, security and IT ask about first, included from day one.
Sign in through your identity provider and keep accounts in sync automatically as people join, move and leave.
Build custom roles, scope them to teams or regions and review grants on a schedule you control.
Every action is recorded and can be streamed to your security tooling in near real time.
Choose where data is stored and processed, with documented sub-processors for each location.
Run on isolated compute and storage with private networking and your own maintenance windows.
A technical account manager, a 15-minute response target for critical issues and quarterly reviews.

More than 200 certified connectors, plus open APIs, webhooks and a Terraform provider for everything else.
Three organisations, three industries and one common result: faster audits with fewer surprises.
 Summit&Co
62%less audit preparation time
Summit&Co replaced spreadsheet evidence with automated control reports across 11 business units.
Read the story Evergreen Health
3.4Mpatient records governed
Evergreen Health enforced least-privilege access in nine weeks without slowing clinical teams.
Read the story Voltra Energy
4xfaster access approvals
Voltra routes contractor requests by risk and now closes most of them in under an hour.
Read the storyUptime SLA, backed by service credits
Enterprise customers worldwide
Hosting regions for data residency
Response target for critical issues
“SaaSyTech gave us one place to prove control to our regulators. Our last examination took four days instead of three weeks, and nothing needed rework.”
 Richard HaleChief Information Security OfficerSummit&Co
“Procurement signed off in one cycle. The security documentation answered every question before we asked.”
 Elena DuarteChief Information Officer, Evergreen Health
“Predictable pricing, a named manager and an uptime record we can show our board. That is rare.”
 Martin VossChief Financial Officer, Voltra Energy
Start with a team plan or talk to us about an enterprise agreement tailored to your requirements.
For departments that need shared workspaces and solid basics.
For organisations that need SSO, automation and stronger oversight.
For global organisations with advanced security and compliance needs.
Need something specific for a vendor review? Our trust team answers questionnaires within five business days.
Yes. Under NDA we share our latest SOC 2 Type II report, ISO certificates and penetration test summaries.
You choose the primary region from 14 locations. Data stays there, and backups remain in the same jurisdiction.
Enterprise plans can bring their own keys from a supported key management service and revoke access at any time.
Connect any SAML 2.0 or OIDC provider in minutes, then enable SCIM to provision and deprovision users automatically.
Enterprise agreements include a 99.99% uptime SLA with service credits and a public status history.
Most organisations go live with a first business unit in four to six weeks, guided by a dedicated implementation lead.
Yes. Data and logs are exportable at any time in open formats, and audit events can stream to your SIEM.
Our legal team works with yours on master agreements, data processing addenda and business associate agreements.
Book a 45-minute walkthrough with a solutions engineer. Bring your security questionnaire and we will answer it live.